Fourteen parts
What KYC verification is, in plain English
KYC verification, short for Know Your Customer, is the regulated process by which a financial institution or other obliged business confirms that a customer is who they claim to be, before and during a business relationship, using reliable and independent sources. It is a set of obligations, not a single product or a one-time document check.
Under the FATF standard, the global baseline that national laws implement, the operative obligation is Customer Due Diligence (CDD) in Recommendation 10. This requires obliged entities to identify the customer and verify their identity from reliable, independent sources; identify and take reasonable measures to verify any beneficial owner; understand the purpose and nature of the relationship; and conduct ongoing due diligence throughout the relationship. "KYC" is the everyday umbrella term for this discipline. "Identity verification" (IDV) is the narrower technical step of proving a claimed identity is real and belongs to the person presenting it.
KYC matters because it is the front door to the entire anti-money-laundering system. Get it wrong and you either let criminals in, which invites fines and real harm, or you turn good customers away at onboarding and lose revenue. For the practical "how we think about running KYC" angle, see our companion piece on KYC meaning and a practical guide to Know Your Customer.
KYC vs CDD, CIP, KYB, and AML
These terms are constantly conflated. Getting them straight is the fastest way to understand the field.
AML is the whole regime: risk assessment, KYC and CDD, transaction monitoring, sanctions screening, suspicious activity reporting, and record-keeping. KYC is specifically the "know who your customer is" part of that regime. CDD is the formal regulatory obligation that KYC delivers, split into simplified, standard, and enhanced tiers. CIP (Customer Identification Programme) is the US rule for the data you must collect up front. KYB (Know Your Business) verifies a legal entity and its beneficial owners, whereas KYC verifies a natural person. Onboarding a company needs both: KYB on the entity plus KYC on the individuals behind it.
Common misconception
KYC is not a one-time document upload
"KYC means I take a photo of my passport once when I sign up, and then I am done."
Regulation explicitly requires ongoing monitoring and keeping CDD information up to date (FATF Recommendation 10; UK Money Laundering Regulations 2017, Regulation 28). The modern name for doing this continuously rather than on a fixed calendar is perpetual KYC (pKYC). Passing an automated check once does not end the obligation.
How KYC verification works, step by step
A correct KYC process runs as a lifecycle, not a single gate. Each step feeds the next, and the last step loops back for as long as the customer stays with you.
- Customer Identification Programme (CIP): collect identifying data. In the US, FinCEN's CIP rule requires an institution to collect at minimum four data points before opening an account: full legal name, date of birth, address, and a government-issued identification number. The rule is outcome-based: it does not mandate how you verify, only that you form a "reasonable belief" you know the customer's true identity.
- Identity verification: prove the data is real and belongs to this person. This is where technology sits, across documentary checks, electronic checks, and biometrics with liveness. Detail follows below.
- Risk assessment: score the customer and set the CDD tier. Every customer is scored for money-laundering and terrorist-financing risk across who they are, their country, the product, and the delivery channel. The score sets the depth of diligence.
- Screening: check the verified identity against lists. The identity is checked against sanctions lists, politically exposed person (PEP) lists, and adverse media. This is continuous, not one-off.
- Ongoing monitoring: the part people forget. Transaction monitoring for behaviour inconsistent with the customer profile, periodic or event-driven CDD refresh, and re-screening. UK records must generally be kept for five years after the relationship ends.
How identity verification actually works
Step two of the process, proving the data is real, uses three overlapping families of method.
Documentary verification captures an ID document, authenticates it (security features, machine-readable zone or chip, tamper checks), extracts the data, and matches it to the collected identity.
Non-documentary or electronic verification matches the claimed identity attributes against independent, reliable data sources. In the UK, JMLSG guidance treats a "2+2" check, matching at least two attributes such as name and address against at least two independent, reliable sources, as one accepted way to satisfy Regulation 28 electronically.
Biometric verification and liveness match a selfie to the document portrait (face match), then run a liveness or presentation attack detection (PAD) check to confirm a real, present human rather than a photo, mask, screen replay, or deepfake. PAD is standardised by ISO/IEC 30107, independent labs test to 30107-3, and the key error metrics are APCER (attacks wrongly accepted) and BPCER (genuine users wrongly rejected).
Risk tiers: simplified, standard, and enhanced due diligence
The risk score from step three sets how much diligence a customer gets. Getting the tier wrong in either direction is costly: too little on a high-risk customer invites fines, too much on a low-risk one adds friction and drop-off.
| Tier | When it applies | What it adds |
|---|---|---|
| Simplified due diligence (SDD) | Demonstrably low-risk cases | Reduced or deferred verification within the risk-based approach |
| Standard CDD | The default for most customers | Identify and verify the customer and any beneficial owner, understand the relationship |
| Enhanced due diligence (EDD) | PEPs, high-risk or FATF-monitored jurisdictions, complex or opaque ownership | Source-of-funds and source-of-wealth checks, and senior-management sign-off |
What documents and data KYC requires
Exact requirements vary by jurisdiction and risk tier, but a standard individual KYC check typically collects the following.
- Full legal name
- Date of birth
- Residential address
- A government-issued identification number (for example a passport, national ID, or, in the US, an SSN or equivalent)
- A photo of a supporting identity document for documentary verification
- A live selfie for face match and liveness or PAD
- For higher-risk or corporate cases, source-of-funds or source-of-wealth evidence and beneficial ownership details
Note
A 2025 US flexibility on TIN collection
US banking agencies, with FinCEN's concurrence, issued an order (27 June 2025 for OCC, FDIC, and NCUA-supervised banks, with a companion Federal Reserve order on 31 July 2025) allowing banks to collect the last four digits of a customer's tax identification number from the customer and verify the full nine-digit number through a reliable third party, rather than collecting the full number directly.
The laws that require KYC
KYC is a legal requirement for regulated entities under FATF-aligned national law. The specific rulebook depends on where you operate. FATF requires CDD when establishing a business relationship, for certain occasional transactions above a threshold, on any suspicion of money laundering or terrorist financing, and where there is doubt about previously obtained identification data.
| Framework | What it demands | When it applies |
|---|---|---|
| FATF Recommendation 10 | The four CDD obligations, EDD for higher risk, and ongoing monitoring | The global baseline; national laws implement it |
| US FinCEN CIP rule | Collect four data points and form a reasonable belief in the customer's true identity | Before opening an account at a covered US institution |
| UK Money Laundering Regulations 2017 | Regulation 28 CDD, electronic "2+2" verification accepted, five-year record retention | In force now, as amended including 2025 updates |
| EU AMLR (Regulation (EU) 2024/1624) | A single AML rulebook, occasional-transaction CDD trigger lowered to EUR 10,000, and an EUR 10,000 cash cap | Directly applicable from 10 July 2027 for most obliged entities (10 July 2029 for certain others) |
| eIDAS 2.0 (Regulation (EU) 2024/1183) | Moves KYC towards reusable, wallet-based digital identity credentials | In force since 20 May 2024; wallets available by around December 2026, mandatory acceptance by regulated entities from late 2027 |
Where KYC stands in 2025 to 2026
Three regulatory shifts are live right now. The EU AML package creates a single rulebook (AMLR) directly applicable across all 27 member states from 10 July 2027, and a new EU-level supervisor, AMLA, became operational on 1 July 2025 in Frankfurt. In parallel, eIDAS 2.0 and the EU Digital Identity Wallet push the regulated sector towards verify-once, cryptographically-assured credentials, with wallets available across the EU by around December 2026. In the UK, the Money Laundering Regulations 2017 remain the operative rulebook, and in the US the FinCEN CIP rule is the baseline.
Enforcement is escalating. TD Bank paid roughly 3.09 billion US dollars in October 2024 across US regulators for BSA and AML failures rooted in weak customer controls, and in the UK the FCA fined Starling Bank 28.9 million pounds (announced 27 September 2024) over financial-crime control and sanctions-screening failings. FinCEN's FY2024 Year in Review records 4.7 million suspicious activity reports and 20.5 million currency transaction reports filed, the reporting engine that KYC feeds; without knowing the customer, a report is noise.
Country risk is a moving input. FATF's grey list changed several times in 2025: its June 2025 update added Bolivia and the British Virgin Islands and removed Croatia, Mali, and Tanzania, while its October 2025 update removed Burkina Faso, Mozambique, Nigeria, and South Africa. KYC risk models therefore need refreshing on every FATF plenary.
Note
The market context (present as an estimate)
MarketsandMarkets estimates the identity verification market at roughly 14.34 billion US dollars in 2025, forecast to reach around 29.32 billion by 2030 at about 15.4% CAGR. Market-sizing figures vary materially by research house and scope, so treat this as an illustrative estimate rather than a settled fact.
Why so many customers drop off
KYC is also where compliance cost and customer growth collide. Vendor research from Fenergo reports that around 67% of surveyed institutions in the UK, US, and Singapore lost prospective clients to slow or complex onboarding in 2024, and estimates abandoned KYC processes strip roughly 3.3 billion US dollars a year out of banking. More than 60% of KYC attempts happen on mobile, where failed liveness checks and unclear capture instructions drive drop-off.
As for how long verification takes, there is no single reliable benchmark. In practice, automated electronic KYC (eKYC) can complete in seconds to minutes for straightforward individuals, while complex, high-risk, or corporate cases can take days to weeks because of manual review, beneficial-ownership unwinding, and enhanced due diligence.
How AI is transforming KYC for the better
AI is now core to making KYC both more accurate and less painful. In verification specifically, AI is used to authenticate documents and detect forgery at scale, spotting manipulation invisible to the human eye; to match faces and detect liveness or presentation attacks, measured against ISO/IEC 30107-3 error rates; to score risk and tier CDD by combining identity attributes, country risk, product, and channel; to cut false positives in noisy sanctions, PEP, and adverse-media screening so analysts spend time on real hits; and to reduce onboarding friction, which is itself a commercial and compliance win.
AI on the defender’s side
Where Zenoo's AI genuinely applies
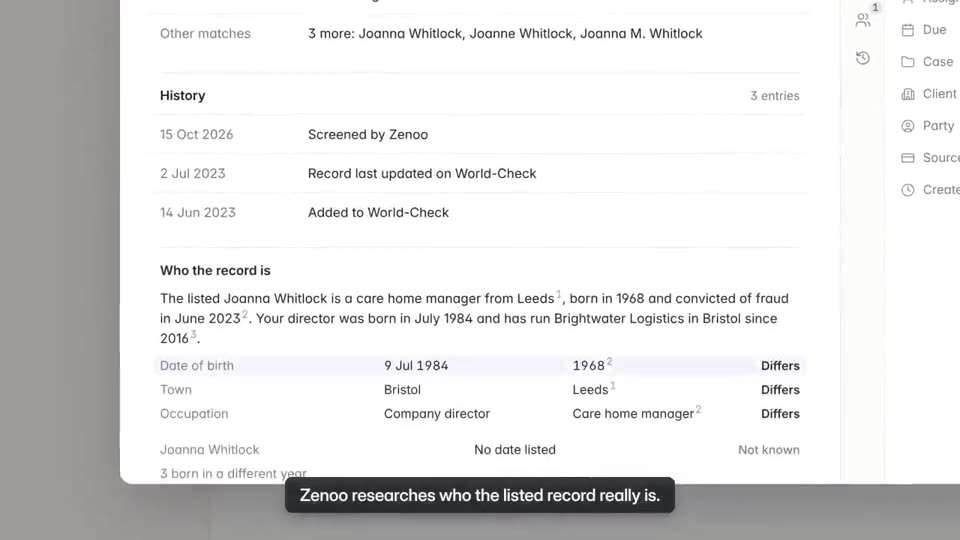
Zenoo does not replace your verification vendors. It orchestrates them and adds an AI analyst layer on top of the results they return. Zenoo runs 10 specialised AI agents that assist analysts, cutting alert investigation from an industry benchmark of 22 hours to about 12 minutes and delivering a 95% reduction in false positives for most teams within 90 days (Zenoo, metrics registry). Honest agent-level capabilities include a KYC Researcher that compresses individual due-diligence research from 1 to 3 hours to under 45 seconds, a Document Classifier recognising 30+ AML and KYC document types in under 15 seconds, pre-classification of up to 80% of screening alerts, and a 209-country risk database with 16 indicators each feeding risk tiering (all Zenoo, metrics registry). These accelerate the analyst's work on top of vendor outputs; they do not perform the underlying document or biometric verification.
How AI is weaponising fraud against KYC
The same generative AI that helps defenders is now the attacker's toolkit. Vendor research from Sumsub's 2025 to 2026 report shows the overall identity fraud rate actually fell (2.6% in 2024 to 2.2% in 2025) while sophisticated multi-step attacks jumped from 10% to 28% of cases, up about 180% year on year. The threat is shifting from volume to quality.
Sumsub also reports deepfake fraud up over 1,100%, synthetic identity document fraud up more than 300% in the US, and a single largest country jump of over 2,100% in the Maldives. Injection attacks bypass the camera entirely, feeding a pre-made deepfake video stream straight into the verification pipeline, which is why ISO 30107-style PAD plus injection defence is now essential. Synthetic identity fraud, which blends real and fabricated data to create a person who does not exist but still passes checks, is a growing threat that we cover in a dedicated guide.
AI as the threat
Deepfakes now defeat human verification, not just automated checks
The Arup case (January 2024, Hong Kong) is the canonical example. An employee was deceived by a live deepfake video call impersonating the CFO and colleagues into making 15 transfers totalling around 25.6 million US dollars (HK$200m) in a single day; as of early 2025 no funds had been recovered. It shows that KYC and authentication controls cannot rely on "it looked and sounded like them". Sumsub also warns that agentic AI scams, autonomous fraud agents running whole attack chains, are poised to surge in 2026. No single verification vendor stays ahead of every attack vector, which is precisely why layered, swappable controls matter.
The future of KYC verification
Several attributed forecasts point the same way.
- Regulation converges upward. From 10 July 2027 the EU AMLR single rulebook applies directly across member states, with AMLA supervising and the occasional-transaction CDD trigger dropping to EUR 10,000. Expect other jurisdictions to track the higher floor.
- Identity becomes reusable and wallet-based. EUDI Wallets available across the EU by around December 2026 and mandatory acceptance by regulated entities from late 2027 move KYC towards verify-once, cryptographically-assured credentials.
- The market roughly doubles. Identity verification spend is forecast from about 14.3 billion US dollars in 2025 to about 29.3 billion by 2030 at roughly 15.4% CAGR (MarketsandMarkets, illustrative).
- The arms race shifts to agents. Sumsub forecasts agentic-AI scams surging in 2026 and a continued move to high-quality, multi-step attacks; defenders will lean harder on liveness, PAD, injection defence, and orchestrated multi-vendor coverage.
- Perpetual KYC becomes the norm. Event-driven continuous review replaces calendar-based refresh as the accepted way to satisfy the standing duty to keep CDD current.
Where orchestration fits: your vendors plus Zenoo
The frame here is always "your vendors plus Zenoo", never "replace". Zenoo is a KYC, KYB, and AML orchestration platform. It does not perform document authentication, face matching, liveness or PAD, or sanctions data provision itself. Those come from specialist vendors. Zenoo's job is to connect many of them and run the workflow around them: routing checks to the right provider and failing over when one is down or returns a poor result, keeping one immutable audit trail across all providers, and letting you route by cost as well as coverage. This matters because no single vendor catches every deepfake or covers every country. The metrics registry notes the average institution already uses about 4.7 verification providers (Zenoo, metrics registry).
Honest scope
Where Zenoo does not solve the problem
Zenoo does not decide whether a passport is genuine, whether a selfie is live, or whether a face matches; that is the underlying IDV or biometric vendor's job, and Zenoo orchestrates and records those decisions. Zenoo does not replace your legal obligation to run a compliant CIP and CDD programme or to file reports; it helps you operate it. Zenoo does not itself provide sanctions, PEP, or adverse-media data; it connects to providers that do. And Zenoo is not a magic deepfake detector; defeating deepfakes and injection attacks depends on the specialist detection vendors Zenoo routes to, plus keeping that roster swappable so you can add the best detector as threats evolve.
Where this fits, honestly
From reading about it to running it.
Zenoo orchestrates your KYC, KYB, and AML vendors behind one workflow: routing checks to the right provider, failing over when one is down, and keeping a single audit trail across all of them. Your vendors plus Zenoo, not a replacement.
A live Compliance Hub with fictional data. Nothing you do is saved.